In a watershed moment for international cybersecurity, 26-year-old Canadian national Connor Riley Moucka has pleaded guilty to orchestrating one of the most destructive cybercrime sprees of the modern era. Once identified by security researchers as a high-consequence threat actor, Moucka’s admission of guilt provides a chilling look into the mechanics of a criminal enterprise that compromised the sensitive data of over 165 organizations, including major corporations and federal agencies.
The case—a labyrinthine saga of stolen credentials, international extortion, and digital betrayal—highlights the precarious nature of cloud-based infrastructure and the audacity of a new generation of cybercriminals who operate with total disregard for personal or national security.
The Magnitude of the Breach: A Global Data Heist
Between February and October 2024, Moucka and his co-conspirators executed a systematic campaign of digital theft targeting customers of Snowflake, a prominent U.S.-based software-as-a-service (SaaS) provider. By leveraging compromised login credentials—often targeting accounts that failed to enforce multi-factor authentication (MFA)—the group gained unauthorized access to the cloud environments of massive entities, including TicketMaster, LendingTree, Advance Auto Parts, and Neiman Marcus.
The scale of the operation was staggering. Investigators estimate that the group stole billions of records, siphoning terabytes of data that included banking information, payroll records, Drug Enforcement Administration (DEA) registration numbers, passport information, and Social Security numbers. Perhaps most alarmingly, the group successfully breached telecommunications infrastructure, stealing the call and text history records of more than 100 million AT&T customers.
Chronology: From Digital Shadow to Federal Custody
The rise and fall of Connor Riley Moucka—who operated under the aliases "Judische" and "Waifu"—is a testament to the persistent work of investigative journalists and law enforcement agencies.
- 2020–2023: Moucka, a software engineer based in Kitchener, Ontario, begins his ascent in the criminal underworld, engaging in persistent data breaches and voice phishing attacks against U.S. companies. During this time, he refines his craft and develops his infamous online personas.
- September 2024: KrebsOnSecurity publishes a seminal report documenting the overlap between Moucka (as "Judische") and extremist groups that harass minors. This report establishes a link between his activities and the broader ecosystem of English-speaking cybercriminals.
- October 2024: Following the publication of key investigative findings, the Royal Canadian Mounted Police (RCMP) executes a provisional warrant, arresting Moucka in Ontario.
- July 2025: Cameron "Kiberphant0m" Wagenius, a U.S. Army soldier and key co-conspirator, pleads guilty to his role in the extortion scheme.
- Present Day: Moucka pleads guilty to four criminal counts, including computer fraud, wire fraud, aggravated identity theft, and conspiracy. He awaits sentencing, scheduled for October 27.
Supporting Data: The Anatomy of the Syndicate
The syndicate’s operations were defined by their fluidity and their willingness to engage in "re-extortion"—a tactic where criminals demand further payments after an initial ransom has been paid, under the threat of releasing the already-stolen data.
The Role of Cameron Wagenius
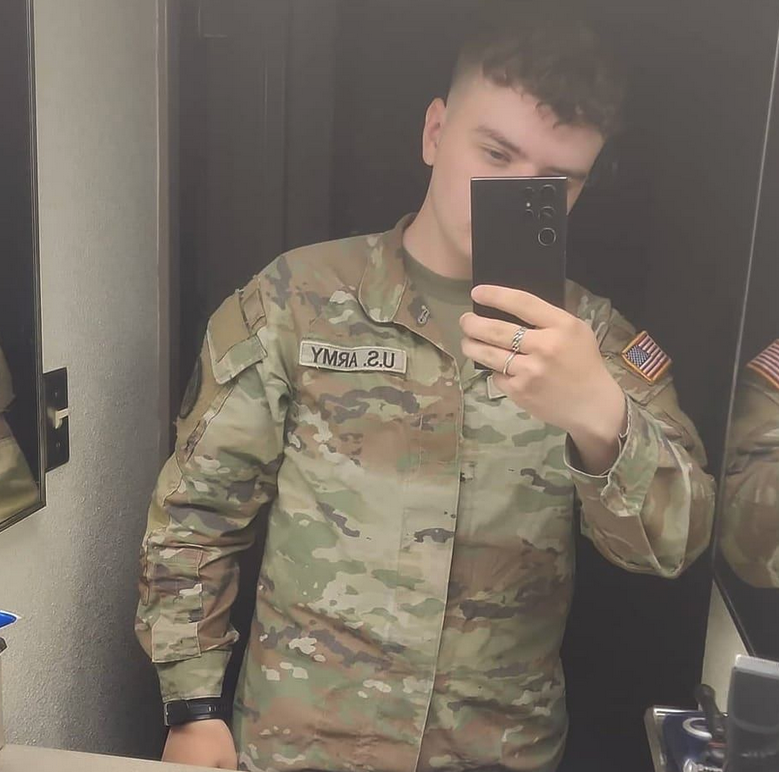
Cameron Wagenius, a U.S. Army soldier stationed in South Korea, served as a vital partner in the operation. Investigations revealed that Wagenius utilized his military background to navigate the dark web, often boasting of his position to other hackers. His activities extended beyond corporate extortion; following Moucka’s arrest, Wagenius reportedly leaked data he claimed were the call logs of then-President-elect Donald Trump and then-Vice President Kamala Harris, along with sensitive schematics purportedly stolen from the National Security Agency (NSA).
The Elusive John Erin Binns
The third pillar of the operation is 26-year-old American fugitive John Erin Binns. Previously indicted for the massive 2021 T-Mobile breach that compromised 76 million records, Binns—known as "IRDev" and "IntelSecrets"—has successfully evaded U.S. justice. Sources suggest that Binns has sought refuge in Turkey, where he recently obtained citizenship. Under Turkish law, he is shielded from extradition, creating a permanent impasse in his prosecution for his role in the Snowflake extortion ring.
Official Responses and Corporate Remediation
The U.S. Department of Justice (DOJ) has been unequivocal in its condemnation of the syndicate’s actions. Prosecutors highlighted the group’s particular cruelty, noting that they harassed government officials and security researchers involved in the investigation. In one instance, the group went so far as to target the personal data of a government officer’s family members to coerce compliance.
For its part, Snowflake responded to the security failures by implementing mandatory MFA across its entire platform and significantly increasing password complexity requirements. The company’s pivot serves as a reminder that even the most robust cloud infrastructure is only as secure as the credentials used to access it.
"The conspirators made over $2.5 million in ransom payments," the DOJ stated, emphasizing that the financial motive was only secondary to the destruction of personal privacy for millions of Americans.
Implications for the Future of Cybersecurity
The Moucka case marks a fundamental shift in how the industry views the "insider-outsider" threat. The inclusion of an active-duty soldier and a veteran of high-profile data breaches suggests that cybercrime is no longer a fringe hobby, but a sophisticated, multi-national industry.
The MFA Imperative
The primary technical lesson of the Snowflake breach is the absolute necessity of multi-factor authentication. Organizations that viewed MFA as an "optional" security layer learned a multi-million-dollar lesson in the cost of convenience. Modern security frameworks now treat MFA as the baseline, not the pinnacle, of identity access management.
The Jurisdictional Quagmire
The case of John Erin Binns illustrates the growing challenge of digital borders. When cybercriminals can obtain state-level protection through citizenship in countries that refuse extradition, the global legal system faces a crisis of enforcement. The ability of such actors to "resurface" and continue their operations highlights the need for more aggressive international cooperation on cyber-sovereignty.
Legal Precedent and Sentencing
As Moucka faces a potential 30-year sentence and a mandatory minimum for aggravated identity theft, the legal system is setting a high bar for cybercrime sentencing. These penalties are designed to serve as a deterrent, yet the lure of millions in ransom remains a powerful enticement for those with the technical skill to bypass security.
Conclusion: A Cautionary Tale
The saga of Connor Riley Moucka, Cameron Wagenius, and John Erin Binns is far from over. While the ringleader sits in a jail cell awaiting his fate and his co-conspirator prepares for sentencing in 2026, the data they released remains in the wild. The millions of individuals whose personal information was exposed now face a lifetime of potential identity theft risks.
As we move forward, the "Snowflake Extortion" will be cited in textbooks and corporate boardrooms alike as the moment the cloud industry grew up. The era of loose credentials and unchecked access is coming to a close, replaced by a more disciplined, if more restrictive, digital landscape. However, as long as there are individuals with the technical acumen and the lack of moral compass displayed by the members of this syndicate, the digital world will remain a battlefield where the next breach is only one stolen credential away.