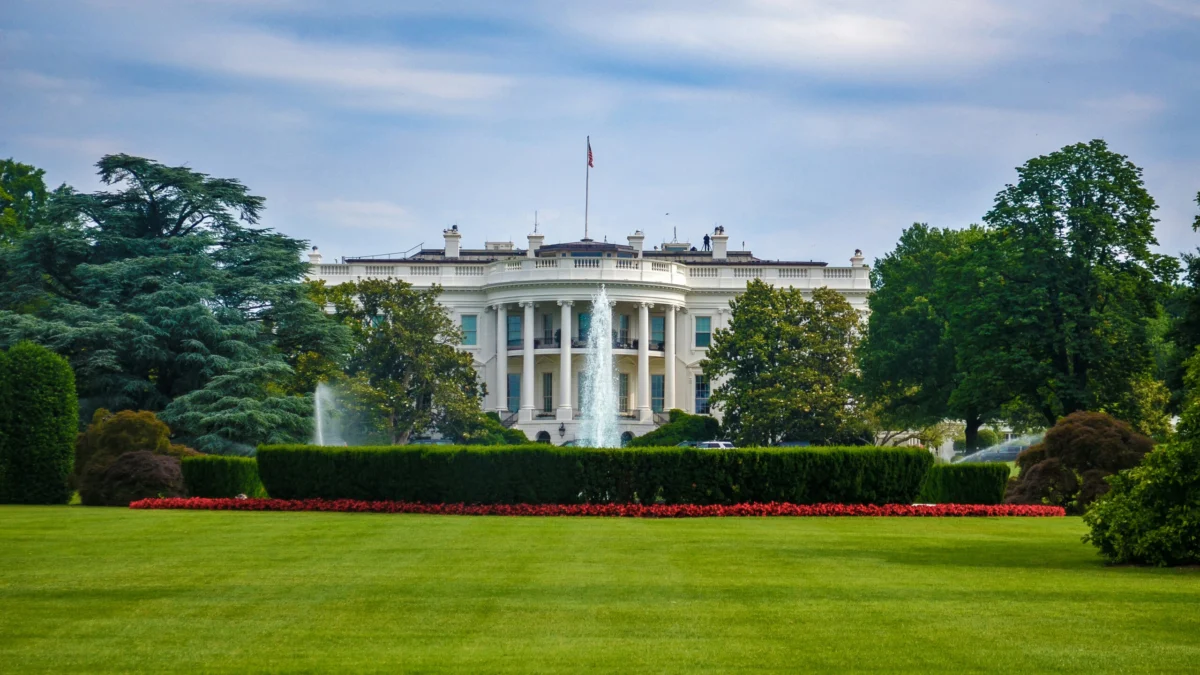
In a startling revelation that underscores the fragility of modern digital perimeters, security researchers have detected the presence of residential proxy software operating from within the Executive Office of the President of the United States. The discovery, documented by the Residential Proxy Observatory—a project spearheaded by the cybersecurity firm Layer3 Intel—highlights a growing trend in which sensitive, high-security networks are being co-opted by global proxy networks without the knowledge of their administrators.
The finding, which centers on the network identifier AS2650, registered to the White House, suggests that even the most protected environments are not immune to the proliferation of "proxyware." While residential proxies are often marketed as legitimate tools for market research or ad verification, their presence inside a core government network raises significant national security questions regarding data exfiltration, unauthorized traffic routing, and the potential for malicious actors to leverage government IP addresses to mask illicit activities.
The Mechanics of the Breach: What Are Residential Proxies?
To understand the gravity of this situation, one must first understand the nature of residential proxies. Unlike traditional data center proxies, which originate from known server farms, residential proxies use the IP addresses of real-world home or business internet connections. This makes traffic originating from these nodes appear legitimate to websites and security filters, as it seems to be coming from a residential ISP rather than a suspicious server.
When an unsuspecting device is infected with proxyware, it becomes an "exit node." Third-party users—who may include legitimate businesses, but also cybercriminals and state-sponsored hackers—pay to route their traffic through these hijacked devices. The device owner is often unaware that their bandwidth is being sold off, effectively turning their hardware into a conduit for someone else’s internet activity. In the case of the White House, this means that traffic associated with the President’s office could be used to facilitate anything from benign web scraping to high-level cyberattacks, all while masking the true origin of the perpetrator.
Chronology: From Discovery to Public Disclosure
The investigation into the White House network began as part of a broader surveillance initiative by Layer3 Intel. The Residential Proxy Observatory was established specifically to track the global footprint of residential proxy exit nodes, recognizing that these networks represent a "blind spot" in enterprise and government security.
Phase 1: Identification of Anomalous Traffic
Researchers began by scanning public routing tables and analyzing traffic patterns associated with known proxy exit providers. By cross-referencing IP addresses with Autonomous System Numbers (ASNs), the team identified a consistent pattern of residential proxy behavior originating from AS2650. This ASN is exclusively assigned to the Executive Office of the President.
Phase 2: Verification and Correlation
Upon spotting the anomaly, the team verified that the activity was not a temporary misconfiguration. The proxy software was found to be actively routing traffic through White House network infrastructure. The data suggested that one or more devices within the premises had been compromised or inadvertently infected with a proxy-enabled application, likely through a user installing seemingly benign software that included a hidden "share your bandwidth" component.
Phase 3: Broadening the Scope
The discovery prompted the team to expand their research to assess the scale of the phenomenon. They soon found that the White House was not an anomaly, but rather a high-profile example of a global problem. They uncovered proxy activity in unexpected places, including the remote island of St. Helena, suggesting that the proxyware economy has permeated even the most obscure and disconnected corners of the globe.
Supporting Data: The Ubiquity of Proxyware
The findings regarding the White House align with a broader, more alarming trend recently detailed by security firm Infoblox. Their research, Residential Proxies are Hiding in Plain Sight, indicates that proxyware has become a staple of corporate and institutional networks.
The Scale of the Problem
- Widespread Infection: Infoblox’s data shows that thousands of enterprise networks globally are currently hosting residential proxy nodes.
- Silent Persistence: Because proxy software often masks itself as legitimate background tasks or browser extensions, it can persist for months or years without triggering standard antivirus alerts.
- The "Double-Dip" Problem: Users often install free software—such as free VPNs, browser-based games, or "utility" apps—that explicitly include a clause in the Terms of Service allowing the developer to monetize the user’s connection. The user gains free access to an app; the developer gains a valuable residential IP address to sell on the black market.
The Residential Proxy Observatory has tracked millions of these nodes worldwide. When categorized by infrastructure, the data shows that government and critical infrastructure providers are increasingly appearing in the dataset, a trend that suggests a significant failure in endpoint management and software supply chain security.
Official Responses and Administrative Silence
As of the date of this publication, official comment from the White House regarding the AS2650 compromise remains limited. Cybersecurity experts note that public acknowledgment of such breaches is a delicate process, often involving internal forensic audits that can take weeks or months to complete.
However, the Department of Homeland Security (DHS) and the Cybersecurity and Infrastructure Security Agency (CISA) have long warned against the risks of "shadow IT"—software installed by employees without the vetting of the IT department. While the White House maintains some of the most stringent security protocols in the world, the human element remains a significant vulnerability. Whether the proxyware was introduced via a personal mobile device, a workstation, or an IoT device connected to the network, the incident serves as a stark reminder that even a "hardened" perimeter can be bypassed by a single unauthorized installation.
Implications: A New Frontier in Cyber Espionage
The presence of a residential proxy node in the White House carries profound implications for international cybersecurity.
1. Masking Malicious Activity
If a state-sponsored actor uses a proxy node inside the White House to launch a Denial-of-Service (DoS) attack against a foreign government or a private corporation, the forensic trail will point back to the White House. This could create a "false flag" scenario, complicating diplomatic relations and potentially leading to retaliatory cyber operations against the US government.
2. Data Exfiltration
Residential proxies do more than just route traffic; they effectively provide an entry point into the local network. While the software is primarily designed to facilitate traffic routing, sophisticated versions can be weaponized to exfiltrate data from the local machine, potentially compromising sensitive documents or communications.
3. The Collapse of Network Trust
For decades, cybersecurity has relied on the concept of "trusted networks"—the idea that traffic coming from within an organization’s internal IP range can be treated with more leniency than external traffic. The existence of proxyware destroys this trust. If the internal network is compromised, internal traffic can no longer be assumed to be safe, forcing organizations to move toward "Zero Trust" architectures at a much faster pace than previously anticipated.
4. Global Interference
The discovery on St. Helena demonstrates that no location is too remote for the proxyware industry. By turning devices into exit nodes, the operators of these networks have created a global, decentralized "botnet-for-hire." This allows bad actors to shift their point of origin dynamically, making it nearly impossible for traditional IP-based blocking methods to keep up.
Moving Toward a Solution
The discovery within the White House should serve as a wake-up call for both the public and private sectors. Security professionals suggest a three-pronged approach to mitigating the risk of residential proxy software:
- Endpoint Detection and Response (EDR): Organizations must update their EDR solutions to specifically look for and block the execution of known residential proxy binaries.
- Stricter Network Controls: Implementing robust egress filtering is essential. By monitoring and restricting the types of traffic allowed to leave the network, administrators can identify and sever the connections used by proxyware.
- User Awareness and Policy: Most proxyware enters the network through employee-installed applications. Strict enforcement of "No-Install" policies on government devices, combined with rigorous vetting of any third-party software, is the only way to ensure that such "moles" do not take up residence in sensitive infrastructure.
Conclusion
The infiltration of the White House network by residential proxy software is a clear indicator that the digital landscape has changed. We are no longer dealing with simple viruses or phishing attacks; we are dealing with a complex ecosystem of "infrastructure-as-a-service" where anyone with a credit card can rent the internet connection of a high-value target.
The fact that this software was found at the heart of the US administration is not necessarily an indication of a sophisticated state-sponsored hack—it is more likely a reflection of the pervasive nature of modern software monetization and the oversight of endpoint security. However, the potential consequences of such a vulnerability are no less severe. As the lines between legitimate internet tools and malicious proxyware continue to blur, the need for heightened vigilance and a radical reassessment of how we define a "trusted" device has never been more urgent.